Security at Carson
Carson reads your customer conversations, so we treat them as the most sensitive data your company has. Each workspace is isolated and encrypted inside Carson, hosted on US-based cloud infrastructure, and never used to train AI models. Session replays are held by our product analytics vendor, also in the US, outside that isolation. Close your workspace and your content and backups are gone within a month, and session replays 30 days after they were recorded.
- Independent audit
- SOC 2 Type IIReport available on request.
- EU and UK data protection
- GDPRProcessor terms and standard contractual clauses in the DPA.
- California privacy law
- CCPAService provider terms. No sale or sharing of personal information.
What we commit to
Encrypted in transit and at rest in Carson
TLS 1.2 or higher over public networks, encryption at rest once it lands in Carson.
Your workspace is isolated
Every analytics query is scoped to one workspace at the application layer. Session replays, held by our product analytics vendor, sit outside that isolation.
We never train AI on your data
Language models receive bounded excerpts for one task, with your organization name, the name of the person asking, your onboarding company background and similar operating context. The providers are barred from training on any of it, and from keeping it beyond the request apart from a short-lived prompt cache that can include themes and signal descriptions derived from your content.
Hosted in the United States
US-based cloud infrastructure for storage and processing.
You can close your workspace
A workspace administrator can close it in Settings or by emailing the support address in Section 11 of our privacy policy, and your content and backups are gone within one month, apart from one model-keyed cache and session replays, both noted in the FAQ below.
We tell you within 48 hours
If a breach affects your data, your workspace admins hear from us within 48 hours of us confirming it.
Staff access is narrow and reviewed
Among our staff, only those who run, support and improve the service can see your data, session replays included, through single sign-on with MFA, with access rights reviewed regularly.
Tested continuously
Vulnerability and dependency scanning, static analysis, cloud posture monitoring, and regular third-party penetration tests.
How your data flows
Carson reads your conversations into a store isolated per workspace and analyses them there. The diagram shows what leaves, and where it goes.
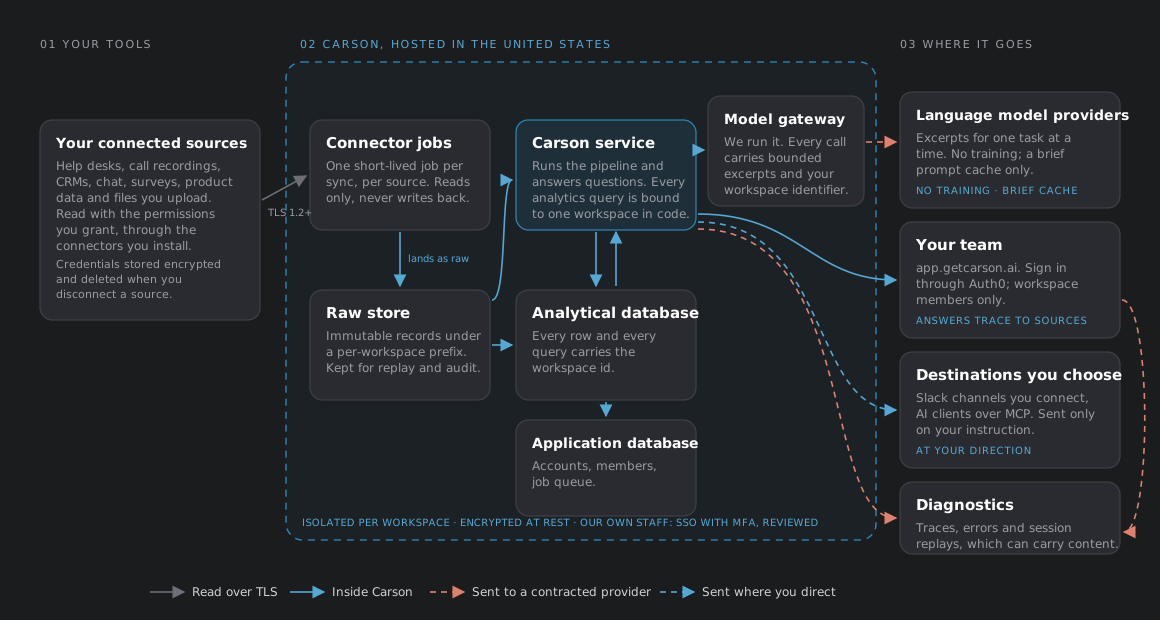
Open the diagram full size (opens in a new tab)
Stays inside your workspace
- Every source is read over TLS into a store isolated per workspace and encrypted at rest.
- Hosted on US-based cloud infrastructure.
- Inside Carson, only members of your workspace and the staff who run, support and improve the service can see it.
What leaves, and why
- Language models receive the bounded excerpts needed for one task, plus your organization name, the name of the person asking, your onboarding company background and similar operating context.
- Providers are contractually barred from training on inputs, and from retaining them beyond the request apart from a short-lived prompt cache that can include themes and signal descriptions derived from your content.
- Requests carry your workspace identifier, the short address confirmed when your workspace was created, for cost tracking and to tell the model which workspace it is in.
- Findings go where you send them: the Slack workspace you connect and AI clients you authorize.
- Traces and error reports go to our monitoring vendors and can carry fragments of content.
- Session replays record what you see in the app, including your content, with fields masked as you type into them, and what our staff see when they open your workspace. They go to our product analytics vendor, which keeps them for 30 days, and we view them to support you and to improve Carson.
What never happens
- We never train AI models on your data.
- We never sell it or share it for advertising.
- Content and backups are deleted within one month of you leaving, and session replays 30 days after they were recorded.
Subprocessors
These vendors process data for Carson. It is the same list as Appendix A of the privacy policy, and the two update together.
| Subprocessor | Purpose | Location | Sees customer content? |
|---|---|---|---|
| Google Cloud Platform | Cloud hosting, storage, databases, logging and AI model inference (Vertex AI) | United States | Yes |
| Auth0 (Okta) | Sign in and identity management | Australia | No |
| Honeycomb | Performance tracing and debugging | United States | Yes, in request URLs and provider error messages |
| HubSpot | Sales and marketing contact with prospects and customers | United States | No |
| Shortcut | Engineering work tracking | United States | No |
| Resend | Transactional email: invitations, sign-in and account messages | United States | No |
| Stripe | Payment processing and invoicing | United States | No |
| PostHog | Product usage analytics, session replay, and error reporting | United States | Yes, in session replays of the screen and in server-side error messages; analytics events are filtered |
| Slack (our support workspace) | Internal support: the message, email address, sign-in intent and sign-in failure reason a visitor submits through the help form on getcarson.ai/help, and the browser details their request carries | United States | No, though findings you choose to post go to your own Slack workspace, as described in Section 6 of the privacy policy |
List last updated October 11, 2026.
Questions we get asked
Your data
Do you use our conversations to train AI?
No. Carson sends bounded excerpts to third-party language models to extract themes and answer questions, and those providers are contractually barred from training on your data, and from retaining it beyond the request apart from a short-lived prompt cache that can include themes and signal descriptions derived from your content. We never train our own models on customer content, and every AI output links back to the conversations it came from.
Where is our data stored?
On US-based cloud infrastructure. Each workspace is logically isolated, every analytics query is scoped to one workspace at the application layer, and data is encrypted in transit over public networks with TLS 1.2 or higher and, in Carson's own systems, at rest. Session replays, which can show your content, are held by our product analytics vendor, also in the United States, outside that isolation.
Who at Carson can see our data?
Only staff who need it to run, support and improve the service, through single sign-on with multi-factor authentication. That includes session replays, which our product analytics vendor holds. Access rights are reviewed regularly. Production and development are fully separated, and our customers' content is never copied into our development or test environments.
What happens to our data if we leave?
A workspace administrator can close your workspace at any time in Settings or by emailing the support address in Section 11 of our privacy policy. Content is removed from production systems within one month and per-customer backups within one month; generated text caches expire within 30 days of last use, a response cache at our model gateway holds requests for up to ten minutes, the provider prompt cache is held for a short period the provider controls, currently up to an hour, and the embedding cache at our gateway is keyed by model rather than workspace and is not purged per workspace. Session replays, which can show your content, are deleted by our analytics vendor 30 days after they are recorded, not sooner. A record of the closure is kept after the content is deleted: when it happened, and the user ID of the administrator who closed it until that person's own account is deleted. The user IDs of the members it removed are kept for 30 days, then deleted. For the first 24 hours after a closure, we also keep the removed memberships and claimed email domains so that support can reopen the workspace; a reopen is noted on the closure record. Billing records are kept for the period the law requires.
Security practices
What certifications do you hold?
Carson is built and operated by Kapiche Pty Ltd, which is audited against SOC 2 Type II and CSA STAR and runs GDPR and CCPA programs. Carson runs on the same controls, infrastructure and team.
How do you test your security?
Continuous vulnerability and dependency scanning, static analysis, cloud posture monitoring, and regular third-party penetration tests. We also run a responsible disclosure program; the address is at the bottom of this page.
How would we hear about a breach?
Without undue delay, and within 48 hours of confirming it, by email to your workspace admins.
Do you back up our data?
Daily database backups and per-customer backups, tested periodically for restorability. Our recovery time objective is 24 hours.
Documents on request
We share these by email with prospects and customers. Tell us who you are and which company you are evaluating for, and we will confirm that before sending anything.
- SOC 2 Type II report
- Penetration test summary
- Data Processing Addendum
- Security questionnaire responses
Report a vulnerability
If you have found a security problem in Carson, tell us before you tell anyone else. Email the address below with what you found and how to reproduce it. We reply within two business days, keep you informed while we fix it, and will not take legal action against research done in good faith. Please do not access data that is not yours and do not disrupt the service for other customers.
How we handle the personal information you send us is described in the privacy policy.